The Kubernetes API boundary sees the workload an actor is requesting now. It must not assume that a green CI run somewhere authorized that request. Kyverno supplies the local image contract: a matching image must have a valid trusted signature and both required attestations before it is admitted.
Allow and deny within the policy scope
Pod request
First evaluate image match and namespace exclusions.
Out of scope
Unmatched registry or excluded namespace: this rule supplies no assurance.
In scope
Require digest pin, signature, SBOM and selected provenance fields.
Allow
Required claims match the configured trust contract.
Deny
A missing claim or trust mismatch rejects the matching request.
Pod request → Out of scopeno scope match
Pod request → In scopescope matches
In scope → Allowclaims satisfy policy
In scope → Denymissing or mismatched claim
Enforce mode applies to matched images and namespaces; outage failurePolicy is a separate operational question.Text equivalent and limits
Unmatched image registries or excluded namespaces do not gain protection from this policy.
Matching Pod images must be digest pinned and have required signature and attestations.
Configured issuer, subject and selected provenance fields must satisfy the policy.
A trust mismatch denies a matching request; success permits admission, not permanent safety.
Read the labeled relationships as the stated contract. Optional connections are dashed and explicitly labeled; comparisons do not imply a sequential handoff. This figure explains inspected code or recorded observations, not current cloud execution.
“ClusterPolicy” describes the Kubernetes resource’s reach, not universal image protection. An image outside that prefix does not receive this rule’s signature/attestation contract. An excluded namespace bypasses these rule matches. Falco and other nonexcluded namespaces are not automatically rejected for unrelated registry images; image matching still applies.
All three rules set required: true, verifyDigest: true, and mutateDigest: false. The chart already supplies the digest; the policy is not documented as a tag-to-digest mutator. It fetches statements from a separate historical metadata repository and requires the accepted signing workflow subject, GitHub issuer, and configured Rekor trust.
Rule 1 requires a valid keyless image signature. Rule 2 requires a valid https://spdx.dev/Document attestation from the same identity. It does not parse package content for vulnerability policy. Rule 3 requires https://slsa.dev/provenance/v0.2 from that identity and compares:
invocation.configSource.entryPoint to .github/workflows/sign-attest.yml.
builder.id to https://github.com/actions/runner.
invocation.configSource.uri to the canonical repository at refs/heads/main.
Kyverno’s attestation conditions evaluate within the predicate body, so the source expressions omit a predicate. prefix. The regression check evaluates those actual expressions against the stored fixture. It is a local condition-shape check, not a full admission test.
The policy does not compare the source commit or materials to an expected promotion source. CI’s contract is stronger on those fields. An accepted admission request therefore establishes the configured image contract, rather than proving its relationship to a particular currently approved source commit.
validationFailureAction: Enforce configures violations to deny matching requests. Missing signatures, wrong identity, absent attestation types, or mismatched required provenance fields should follow the deny path. The owner record reports trusted acceptance and unsigned/mixed/init-container denials. The test-only wrong-trust policy changed signer and source expectations together, so that historical result is one combined negative experiment.
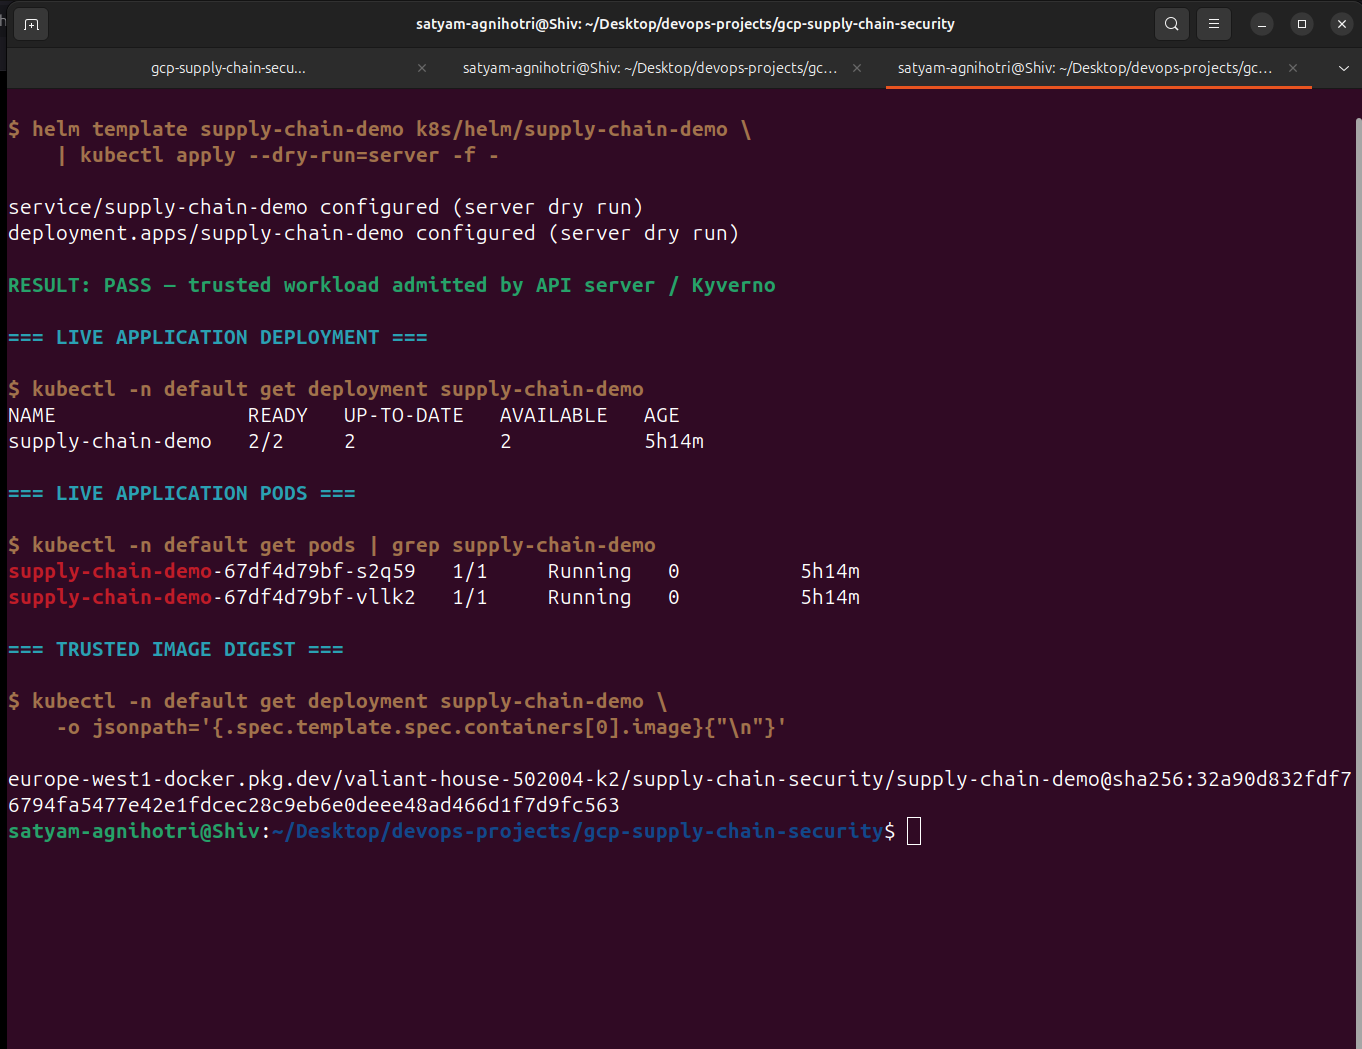
The captured trusted Helm release passed API-server dry run; the application separately had two available replicas.
Recorded result: Service and Deployment configured under server dry run; live Deployment listed 2/2 ready and available.
The signed release passes server dry-run; a separate query reports two available replicas. Select the image for full resolution.
Key limitation: Server dry run does not itself create the observed live replicas; the capture includes separate live-read commands.
Transcript and provenance
Expected in this setup: A workload using the signed selected digest is accepted in the matched namespace.
Historical GCP, europe-west1; current environment not checked · observed 2026-08-23 · source revision unknown; not inferred from the documentation baseline
Selected visible output:
service/supply-chain-demo configured (server dry run)
deployment.apps/supply-chain-demo configured (server dry run)
RESULT: PASS - trusted workload admitted by API server / Kyverno
NAME READY UP-TO-DATE AVAILABLE AGE
supply-chain-demo 2/2 2 2 5h14m
TRUSTED IMAGE DIGEST
sha256:32a90d832fdf76794fa5477e42e1fdcec28c9eb6e0deee48ad466d1f7d9fc563
Full limitations
Server dry run does not itself create the observed live replicas; the capture includes separate live-read commands.
The source commit that built this image and the exact installed policy revision are not established by this screenshot.
Acceptance is historical, not proof of today's controller or workload status.
Visual review of original capture. Collection capture date attributed to docs/my-validation/README.md; this task did not rerun its cloud experiment. The original screenshot is approved for display at the owner’s explicit request for all evidence images and subsequent Cloudflare publication. Original terminal metadata remains visible. No additional pixel redaction was selected or applied. The selected transcript omits incidental prompts without changing the recorded result.
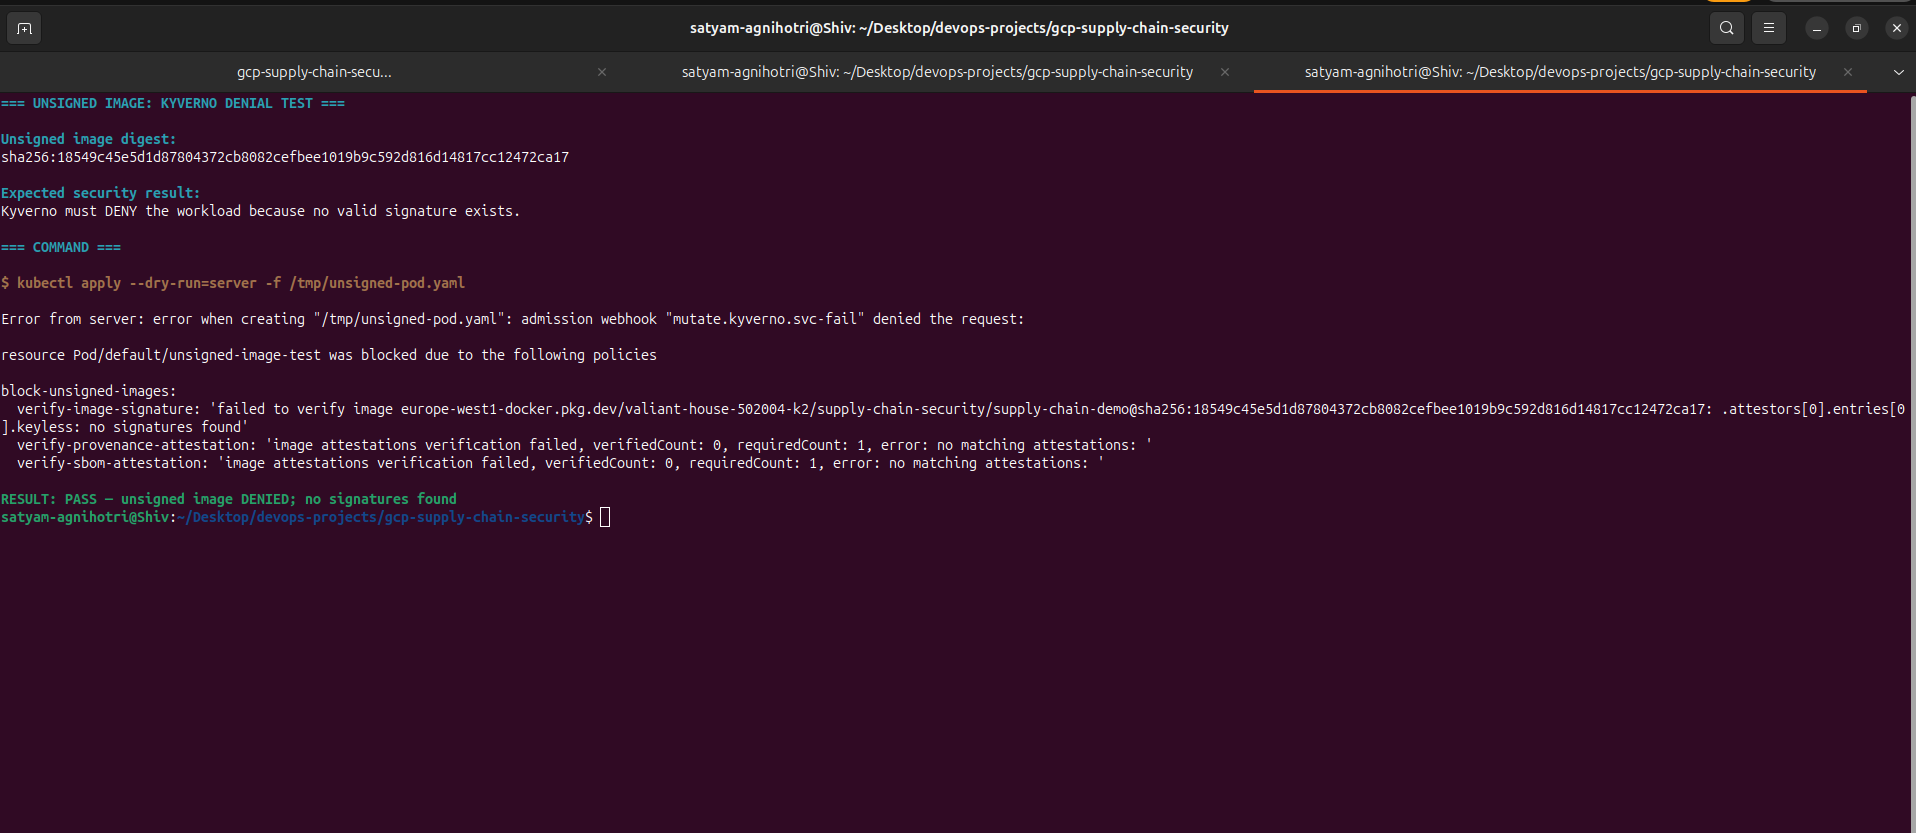
The captured API-server dry run rejected a matching unsigned image.
Recorded result: mutate.kyverno.svc-fail denied the request; signature reported no signatures found and attestations reported no matching attestations.
API-server dry-run rejects the matched unsigned test image. Select the image for full resolution.
Key limitation: This is one server-side dry-run request, not a persisted negative deployment.
Transcript and provenance
Expected in this setup: Reject the matched image without required approved signature and attestations.
Historical GCP, europe-west1; current environment not checked · observed 2026-08-23 · source revision unknown; not inferred from the documentation baseline
Selected visible output:
Unsigned image digest:
sha256:18549c45e5d1d87804372cb8082cefbee1019b9c592d816d14817cc12472ca17
admission webhook "mutate.kyverno.svc-fail" denied the request
resource Pod/default/unsigned-image-test was blocked
verify-image-signature: no signatures found
verify-provenance-attestation: image attestations verification failed, verifiedCount: 0, requiredCount: 1, error: no matching attestations
verify-sbom-attestation: image attestations verification failed, verifiedCount: 0, requiredCount: 1, error: no matching attestations
RESULT: PASS - unsigned image DENIED; no signatures found
Full limitations
This is one server-side dry-run request, not a persisted negative deployment.
Three missing claims occur together; it does not isolate each attestation requirement independently.
Unmatched registries and excluded namespaces were not tested in this capture.
Visual review of original capture. Collection capture date attributed to docs/my-validation/README.md; this task did not rerun its cloud experiment. The original screenshot is approved for display at the owner’s explicit request for all evidence images and subsequent Cloudflare publication. Original terminal metadata remains visible. No additional pixel redaction was selected or applied. The selected transcript omits incidental prompts without changing the recorded result.
These working-boundary observations compare a trusted dry run with a request missing all three claims together. They do not isolate signature-only, missing-SBOM or missing-provenance cases, and they do not test a verifier outage.
The Helm values annotate the admission controller’s Kubernetes ServiceAccount with the verifier GSA. Terraform grants repository reader roles and the narrow KSA impersonation binding. Registry authentication is essential because the metadata repository must be readable even when the application image itself is available.
The stored values do not explicitly configure webhook failurePolicy or timeout. Enforce establishes violation handling; it does not, by itself, prove how the API behaves if the webhook is unavailable. Historical decision records identify Kyverno chart 3.9.0/application 1.19.0, but version-specific defaults and installed webhook configuration must be checked before claiming an outage is fail-closed. This edition leaves that outage behavior unverified.
The background: true setting supports evaluation/reporting of existing resources. It does not retroactively evict running Pods merely because a claim becomes invalid later.
Recorded tests establish regular-container, mixed-container, and unsigned-initContainer outcomes for their specific fixtures. There is no recorded ephemeral-container test. Admission acceptance does not establish that the program will behave safely after it starts, or that policy administrators cannot weaken the rules.