A signature says who made a statement about a digest. To reason about what was built, a verifier also needs structured claims: what packages are present, and what source/build invocation the workflow says produced the artifact. These statements help inspection and policy decisions while retaining the workflow as a trust dependency.
Three claims, three questions
Signature
Authenticates the configured signer’s endorsement of digest D.
SPDX SBOM
Describes detected components for D; does not prove completeness.
Provenance
Records workflow/build/source claims about D; is not a certified SLSA level.
Signed claims authenticate their source. They do not establish vulnerability-free software or an independently verified builder.Text equivalent and limits
Authenticates the configured signer’s endorsement of digest D.
Describes detected components for D; does not prove completeness.
Records workflow/build/source claims about D; is not a certified SLSA level.
Read the labeled relationships as the stated contract. Optional connections are dashed and explicitly labeled; comparisons do not imply a sequential handoff. This figure explains inspected code or recorded observations, not current cloud execution.
The signing workflow runs Syft against the digest it has just signed. It writes sbom.spdx.json, reports the package count, uploads the file as a GitHub artifact with 90-day retention, and calls cosign attest --predicate sbom.spdx.json --type spdxjson against the same image reference.
This is the SBOM required by the verification contract. Its subject binds the signed inventory to the image digest, and the signer ties it to the approved workflow identity. Those properties do not establish package completeness, accurate dependency relationships, license acceptability, or absence of vulnerabilities. The admission policy requires a valid SPDX attestation but has no package-content conditions.
The separate SBOM and VEX workflow generates a CycloneDX source SBOM from app/ and runs supplementary reachability analysis. It is not the image SPDX attestation. Its depscan step uses both continue-on-error: true and || true; the release chain does not depend on this job. Other failures in that job can still make the job red, so its “non-blocking” label means it is outside the build→sign→verify dependency path, not that every step ignores errors. Reports have 30-day retention.
The signing workflow creates a JSON provenance predicate and attests it using slsaprovenance, which the final consumers expect as https://slsa.dev/provenance/v0.2. Its relevant fields are:
The reusable signing workflow path derived from job_workflow_ref
materials
A repository URI and the same source commit
invocation.parameters
Event, Git ref, and caller workflow context
The script requests a GitHub OIDC token with Sigstore audience, decodes the claim payload, and strips repository/ref portions of job_workflow_ref to obtain the entrypoint. This avoids confusing the top-level caller deploy.yml with the reusable workflow that produces the statement. The script-generated predicate is signed by that workflow; it is not a separately audited builder log.
The predicate schema is not a SLSA level. The workflow’s assertions do not prove a hermetic build, independently verified materials, reproducibility, or resistance to a compromised runner. This JSON also does not enumerate every dependency/base image as a source material. A trusted workflow capable of lying can create a well-formed, validly signed false claim.
CI verification compares more of these fields than admission does. It checks the current source commit and matching material in addition to digest, identity, builder, source URI, and entrypoint. Neither consumer explicitly validates the buildType field or every invocation parameter. Read the exact checks instead of interpreting printed provenance as enforced provenance.
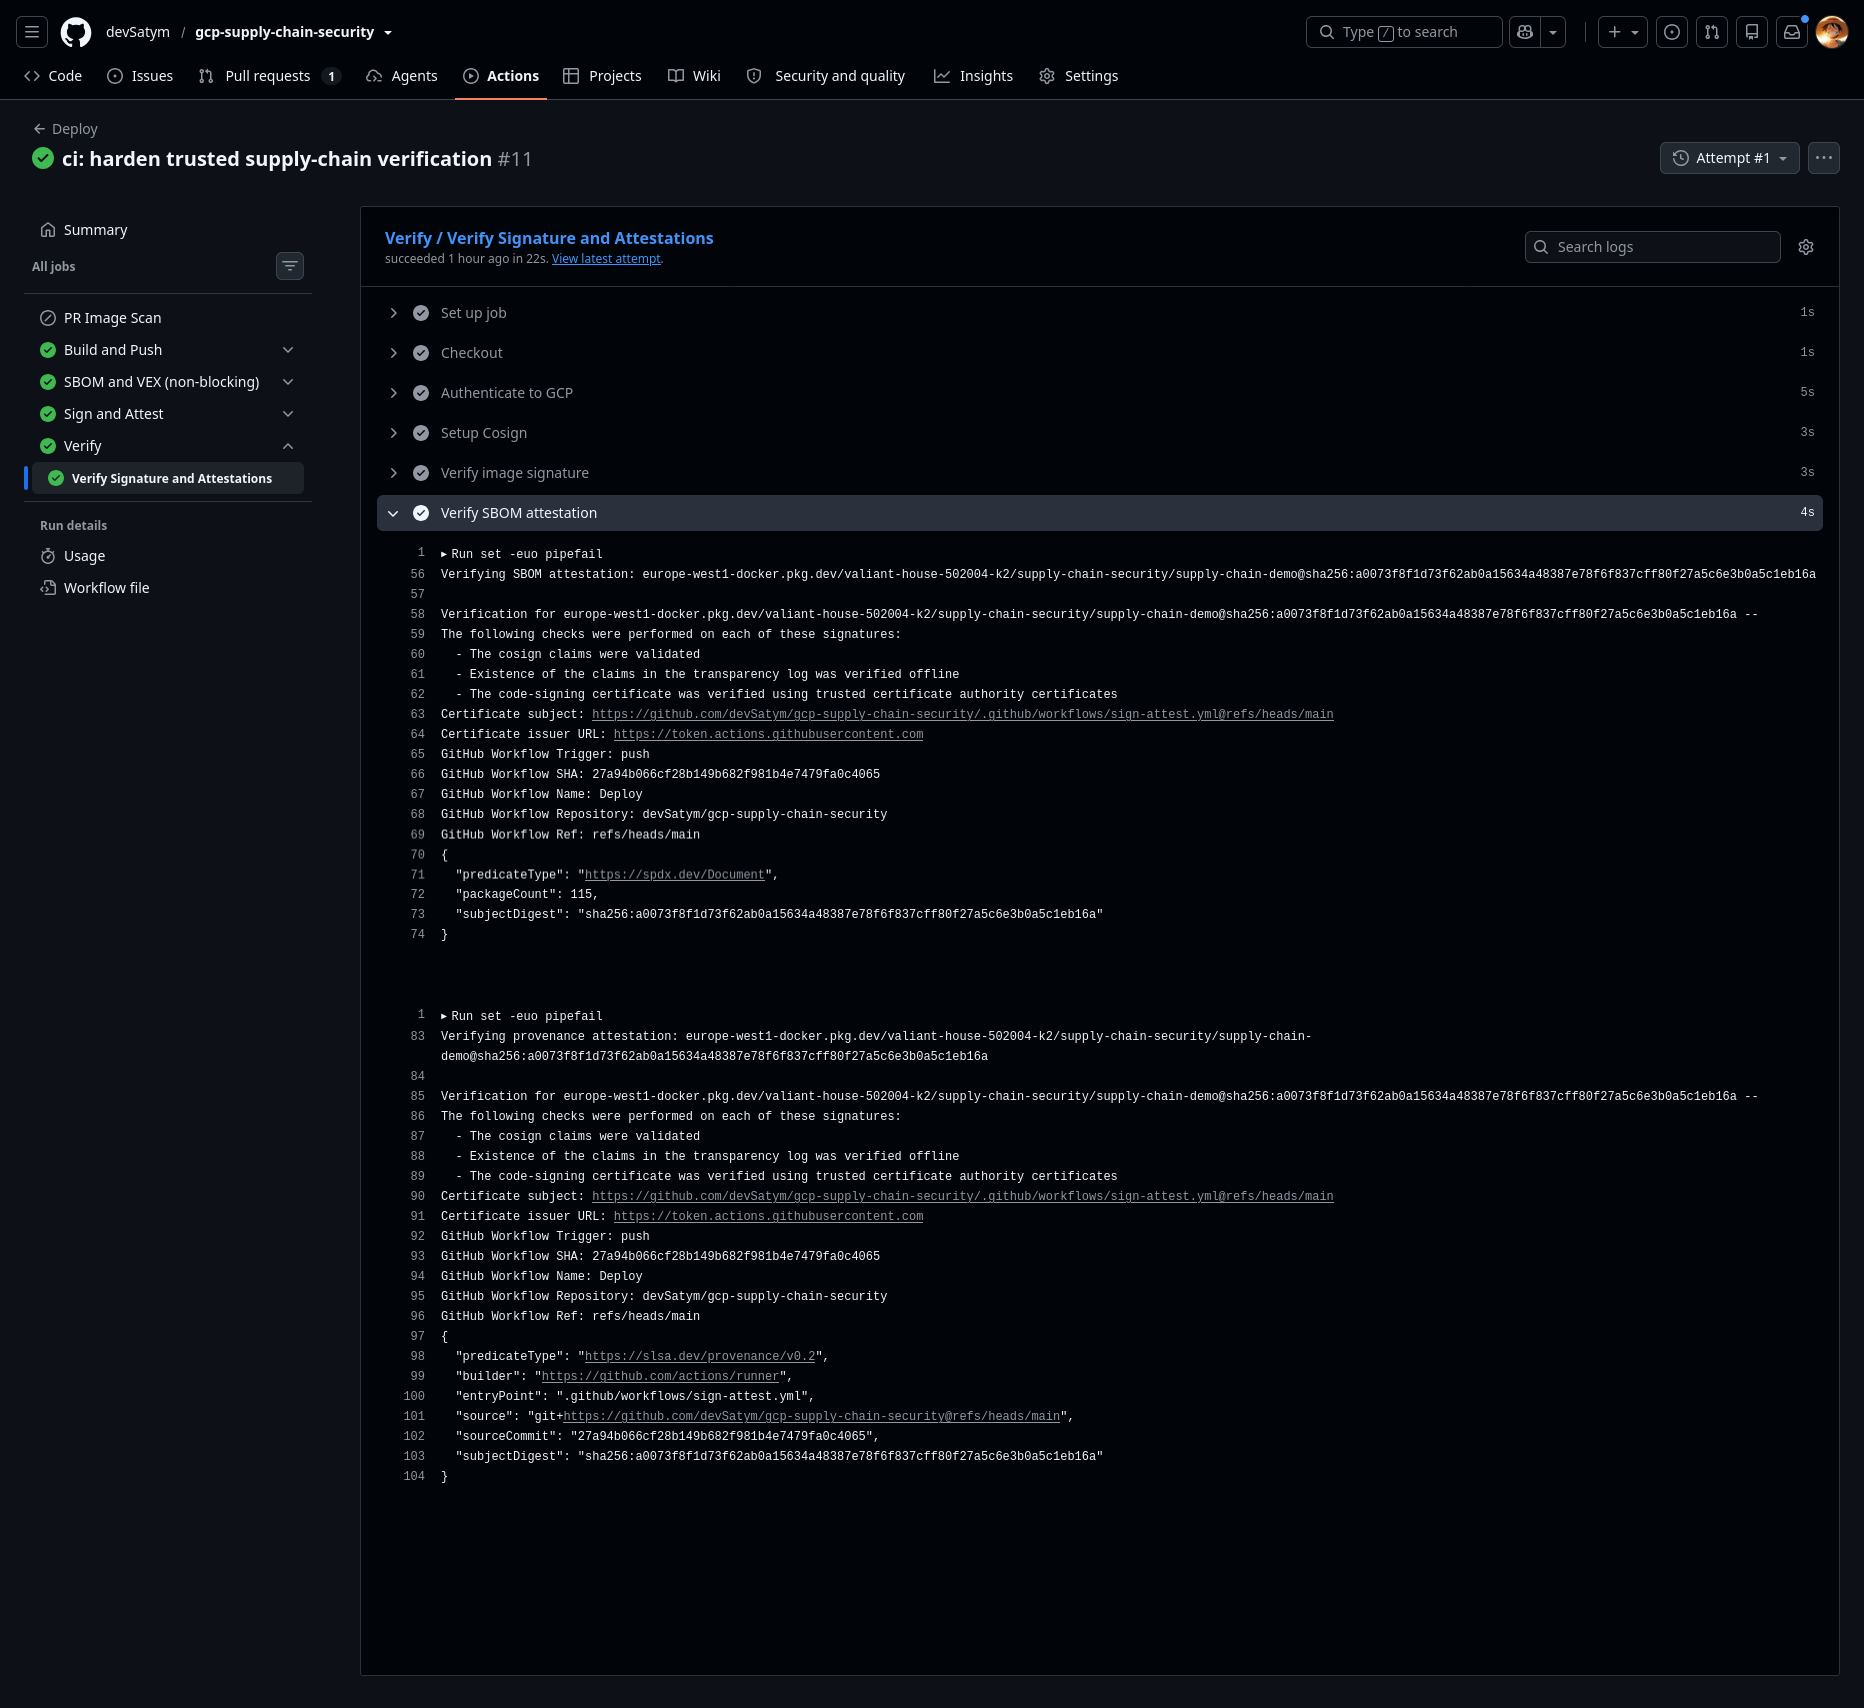
Recorded execution · accepted
The pictured CI verification accepted authenticated SPDX and SLSA v0.2 claims for its digest.
Recorded result: Decoded verification output shows SPDX packageCount 115 and provenance builder/entryPoint/source/sourceCommit fields.
Historical CI output for a0073f8f…; verification confirms the captured claims, not an entire supply-chain assurance level. Select the image for full resolution.
Key limitation: Package count is this capture's output, not a measure of SBOM completeness or package safety.
Transcript and provenance
Expected in this setup: Authenticated claims identify the expected digest, signer, issuer, builder, entrypoint and source.
Historical GCP, europe-west1; current environment not checked · observed 2026-08-23 · source revision 27a94b066cf28b149b682f981b4e7479fa0c4065
Package count is this capture's output, not a measure of SBOM completeness or package safety.
SLSA v0.2 is a schema label; no assurance level established.
This digest differs from the later live-acceptance test digest.
Visual review of original capture. Collection capture date attributed to docs/my-validation/README.md; this task did not rerun its cloud experiment. Unmodified original. Public workflow identity, source commit, digest and historical registry scope retained. No credential or personal workstation path visible.
The record above corroborates the visible SPDX/provenance fields for its pictured a0073f8f… artifact. It is separate from the 32a90d… acceptance test. The website does not use a package count as a security score or claim that attestation presence makes every package safe. Continue to the CI verification handoff to see how these claims become a release-candidate result.