An image can be correctly signed while a statement names the wrong source, a later GitOps change can select a different digest, or a direct Kubernetes request can bypass the CI handoff altogether. CI verification examines the artifact just produced by the run. Admission examines the image in the request now presented to Kubernetes. They enforce a claim at different times and boundaries.
The second check is valuable because deployment state and registry access can change after CI. It is not an independent guarantee that the original workflow was honest: both stages trust the same signing identity and its claims. Understanding the exact field overlap is more useful than counting this as “two layers of security.”
Both trust the same workflow identity; admission does not repeat CI source commit/material matching.Text equivalent and limits
Both paths check the trusted keyless identity and digest-bound artifact claims.
CI additionally matches the invocation source commit and source material against github.sha.
Admission checks builder, workflow entry point and canonical source URI without that commit/material predicate.
Shared workflow/policy authority is a correlated failure dependency; these are not automatically independent roots.
Read the labeled relationships as the stated contract. Optional connections are dashed and explicitly labeled; comparisons do not imply a sequential handoff. This figure explains inspected code or recorded observations, not current cloud execution.
Verify Attestations runs after both build and sign jobs succeed. It authenticates to GAR, installs Cosign, and constructs repository@${inputs.digest} using the build output. It also knows github.sha for the run, so it can compare origin statements with the source it expects.
Each verification shell block uses set -euo pipefail. Cosign checks the certificate subject and GitHub issuer; jq rejects output that lacks a matching statement. A file existing or a command printing fields is insufficient. The final workflow turns field selection into an explicit failure condition.
The expected subject names .github/workflows/sign-attest.yml@refs/heads/main in github.repository; the issuer is https://token.actions.githubusercontent.com. After cosign verify, jq selects signatures whose .critical.image["docker-manifest-digest"] equals inputs.digest. An empty selection errors with no signature matched the expected immutable digest.
The output provides subject, issuer, and signer digest for the summary. Those displayed fields are derived from accepted verification output. They are still a result for one invocation; a historical summary is not ongoing registry verification.
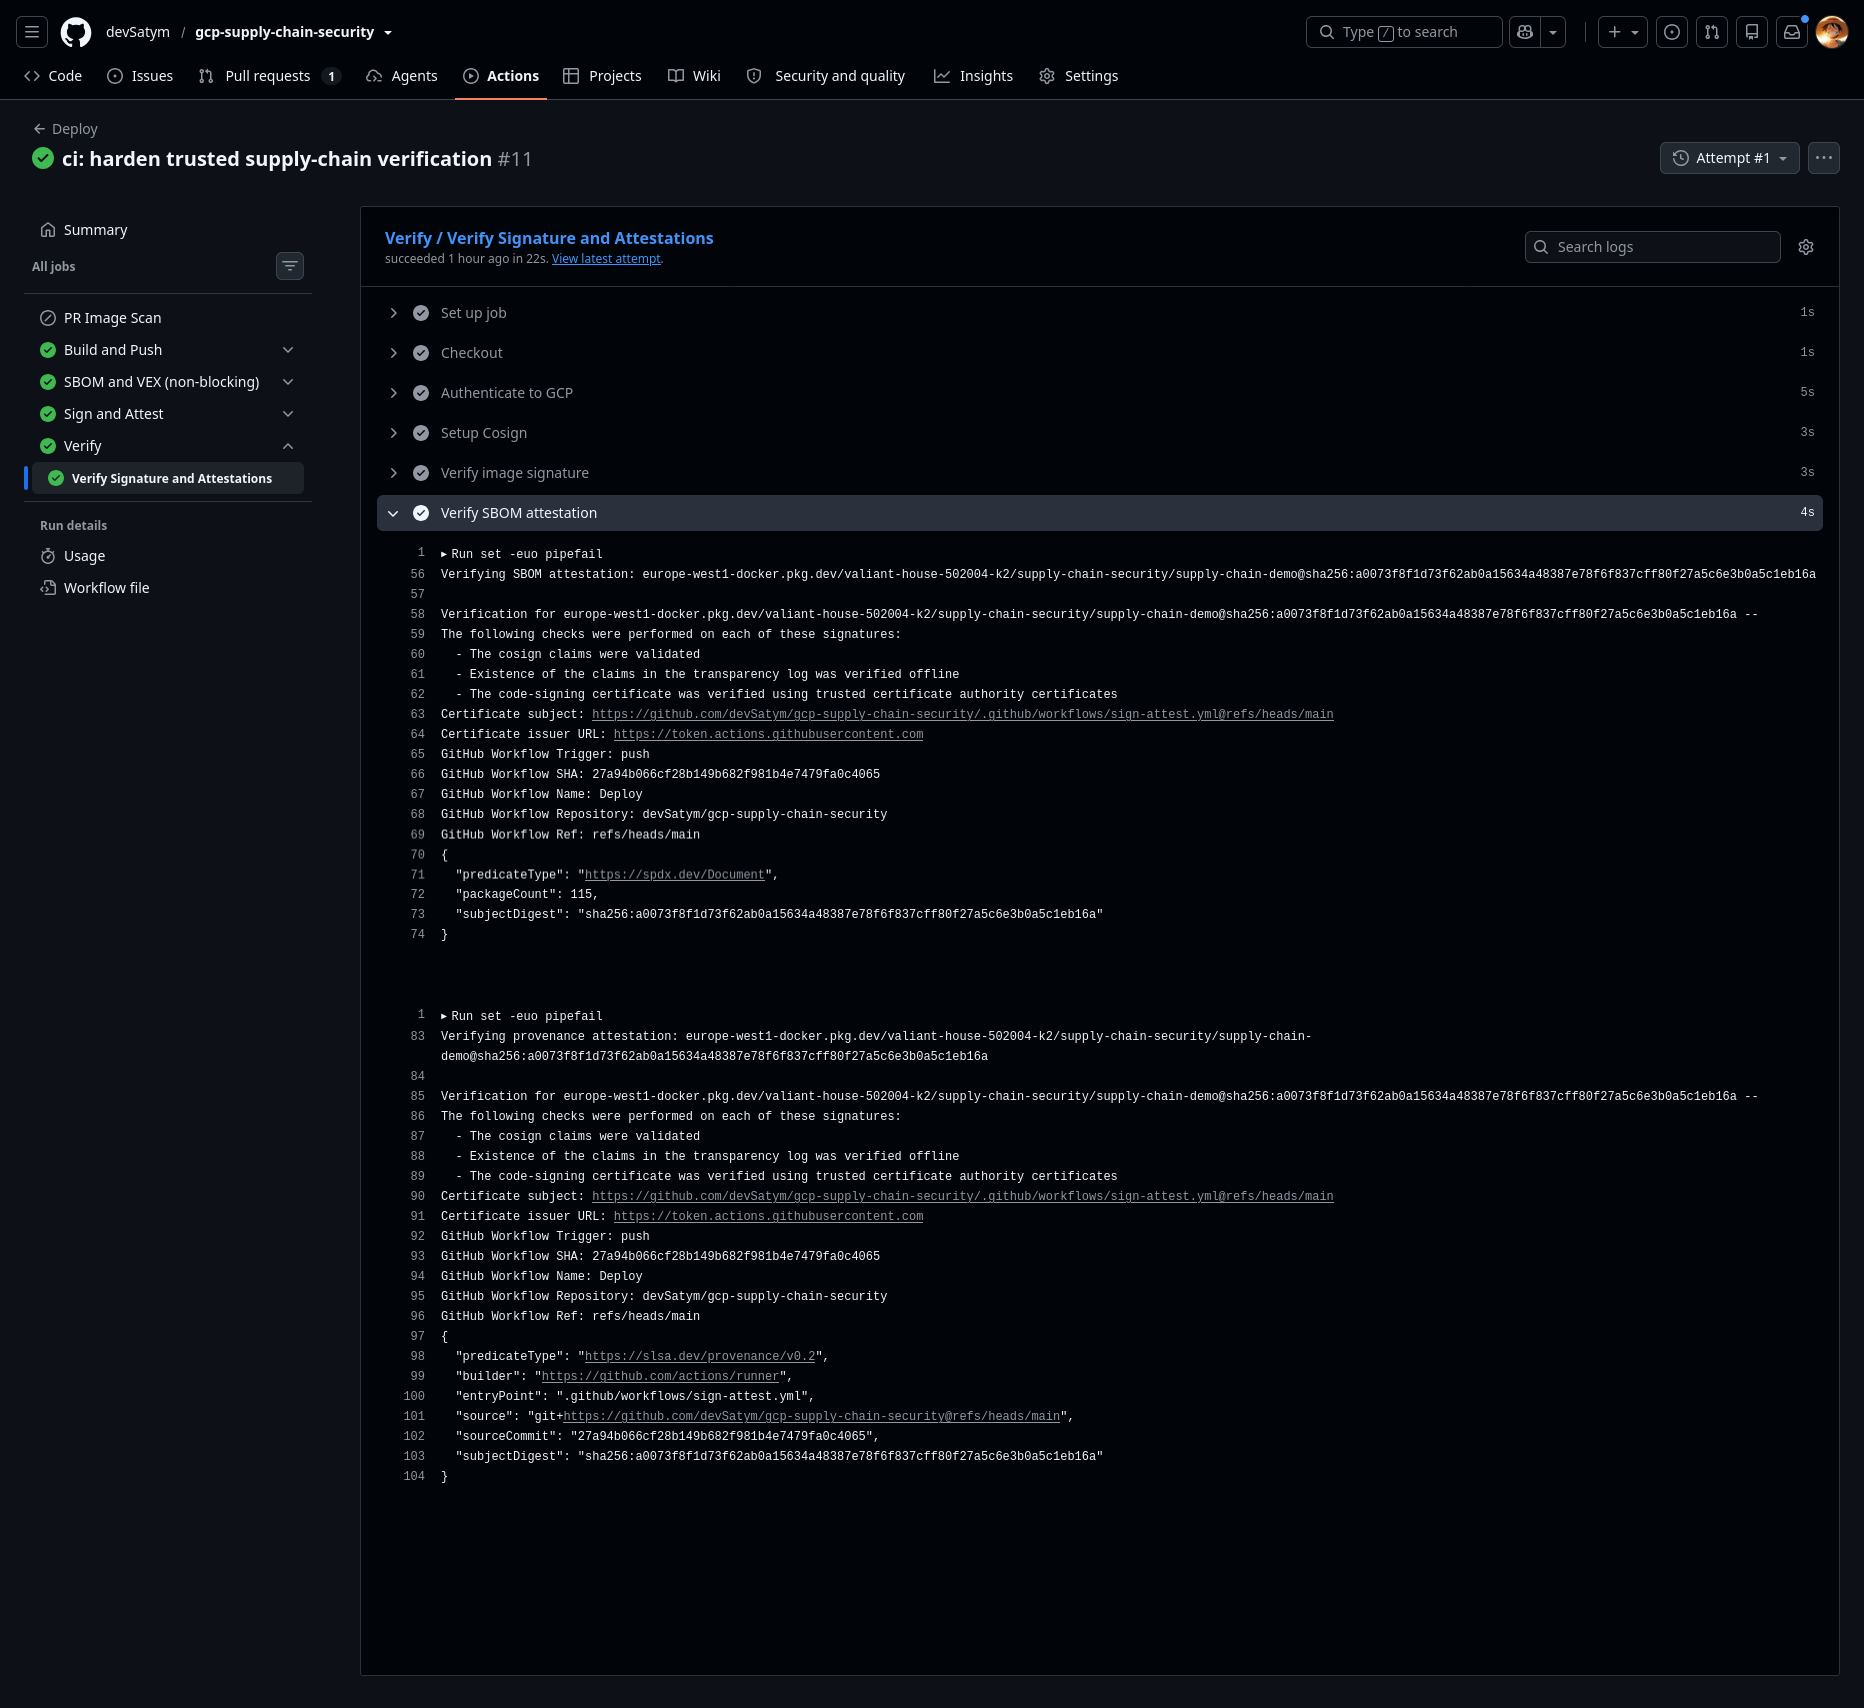
CI calls cosign verify-attestation --type spdxjson with the same certificate constraints. It decodes the envelope payload, requires predicateType == "https://spdx.dev/Document", and requires at least one subject digest to match the built SHA-256 digest. If none matches, the job fails. It prints the package count but does not impose a package-count threshold or inspect package vulnerability/license policy.
The matching rule uses any(.subject[]?), while the summary displays the first subject’s digest. In normal workflow-generated statements there is one image subject; for a multi-subject statement, summary display and matching subject need not be the same entry. This is another reason to evaluate conditions instead of treating the presentation as the entire contract.
CI calls cosign verify-attestation --type slsaprovenance with the trusted subject/issuer and accepts a statement only when all of the following match:
Predicate type https://slsa.dev/provenance/v0.2.
At least one subject SHA-256 equal to the built image digest.
Builder ID https://github.com/actions/runner.
Entrypoint .github/workflows/sign-attest.yml.
Source URI git+https://github.com/${github.repository}@refs/heads/main.
Source digest SHA-1 equal to the run’s github.sha.
At least one material whose URI is the repository without the ref suffix and whose SHA-1 equals the same source commit.
The script explicitly errors if no statement meets this conjunction. It does not enforce buildType, event, workflow display name, or every material. It does not independently reconstruct the image from those materials. A compromised accepted signer can still manufacture matching assertions.
The Kyverno policy requires signature, SPDX, and provenance verification for matching images. It configures the same workflow subject/issuer and verifyDigest: true; its provenance conditions compare builder, entrypoint, and source URI.
Admission does not compare invocation.configSource.digest.sha1 to an operator-selected source commit, nor require a matching repository material. The cluster policy therefore accepts claims from the allowed main workflow/repository without proving that the current Pod selects the source revision checked by a particular CI run. The immutable digest in desired state carries that selection across the handoff, subject to operator review.
This difference is deliberate documentation of the actual source. It would be misleading to copy the stronger CI contract into the admission description or to infer a source-commit allowlist from a source URI.
The release handoff is a candidate, not deployment
The pictured CI verification accepted authenticated SPDX and SLSA v0.2 claims for its digest.
Recorded result: Decoded verification output shows SPDX packageCount 115 and provenance builder/entryPoint/source/sourceCommit fields.
Historical CI output for a0073f8f…; verification confirms the captured claims, not an entire supply-chain assurance level. Select the image for full resolution.
Key limitation: Package count is this capture's output, not a measure of SBOM completeness or package safety.
Transcript and provenance
Expected in this setup: Authenticated claims identify the expected digest, signer, issuer, builder, entrypoint and source.
Historical GCP, europe-west1; current environment not checked · observed 2026-08-23 · source revision 27a94b066cf28b149b682f981b4e7479fa0c4065
Package count is this capture's output, not a measure of SBOM completeness or package safety.
SLSA v0.2 is a schema label; no assurance level established.
This digest differs from the later live-acceptance test digest.
Visual review of original capture. Collection capture date attributed to docs/my-validation/README.md; this task did not rerun its cloud experiment. Unmodified original. Public workflow identity, source commit, digest and historical registry scope retained. No credential or personal workstation path visible.
The displayed record corroborates the fields visible in its own historical invocation. Source inspection establishes the final verifier contract; it must not be retroactively assigned to an older artifact that lacks its own matching execution record.
The workflow summary marks verification passed only after its checks. The orchestrator has no job that updates Helm values, opens a promotion PR, runs kubectl, or calls Argo CD. Its result is a candidate artifact that meets this run’s verification contract.
The later strict CI record reports a verified a0073… digest while Helm remains on the earlier 32a90… digest. This is exactly the separation between artifact verification and deployment authorization. Do not attribute the final strict checks to the earlier artifact unless its own execution record supports that conclusion.
Both verifiers depend on GitHub’s accepted identity, Sigstore trust, registry metadata availability, and policy/code integrity. A compromised GitHub workflow that retains the accepted subject can sign a malicious image and fabricate matching provenance. A compromised policy administrator can weaken admission. An unavailable verifier or registry creates a different failure path whose API behavior must be inspected separately from content-denial tests.